Penetration testing for startups

Your first enterprise deal is stuck on a security review. Let's clear it

Can you prove your app is secure? A customer's security questionnaire, a SOC 2 audit, or an investor's diligence will demand it. Siemba runs your first penetration test with in-house certified engineers, hands you a signed report you can share, and keeps it true as you keep shipping.

SOC 2 Type II Certified G2 rating 4.7 out of 5 stars Gartner Hype Cycle 2026 MSSP certified OSCP certified CEH certified CPENT certified CPPT certified LPT certified

Big 4 and global consulting firms bring us in to pentest their government and enterprise clients. Join Our Partner Program.

The things that catch startups off guard

Whether you're standing up your first real security program, or you're the consultant or vCISO running one for someone else's startup, the surprises look the same.

Revenue at risk

A deal stalls on a security questionnaire

A six-figure contract pauses on a vendor security review, and nobody on the team has ever filled one out before.

No coverage

No security hire yet, but customers are asking

Buyers want proof your app is tested. You don't have a security team, and hiring one isn't this quarter's problem to solve.

Stale on arrival

Shipping fast means shipping exposed

Weekly releases outpace a point-in-time pentest that's already out of date by the time the report lands.

Proves nothing ongoing

A once-a-year report proves nothing today

It's out of date by month two, usually before your next release even ships, let alone the one after.

Time you don't have

Compliance reads like a second full-time job

SOC 2, PCI DSS, HIPAA, evidence collection. It eats hours nobody on a small team actually has to spare.

Doesn't scale

Freelance pentesters don't grow with you

A one-off engagement covers today's app, not the one you'll have shipped by next quarter, or the deal after that.

A pentest isn't just security. It's how the deal closes

"How will you make sure our data is protected?" is now a standard question in every enterprise sales conversation, driven not only by regulation, but by reputation and liability.

A third-party pentest report is how a startup answers it with evidence instead of assurances, and how it signals resilience and compliance to the customer on the other side of the table.

SOC 2 Type II Vendor security questionnaires Third-party risk (TPRM) reviews Investor diligence

Talk about your security posture first

Raise it before the buyer does. It shows you're on top of the thing they're worried about.

Show how often you run third-party tests

Independent testing on a cadence signals a real security roadmap, not a one-time box-check.

Provide evidence: reports and attestations

A signed third-party report plus an attestation of remediation turns claims into proof.

Share results on an ongoing basis

Short release cycles mean buyers want current evidence, not last year's certificate.

Where deals stall

Every enterprise deal hits the same gate

The sales cycle moves fast, right up until the security review. Without a third-party pentest report, the deal doesn't move. With one, it does.

On track Blocked on a pentest report Cleared by Siemba

Start with your first pentest. Grow into continuous

Every startup's security journey starts with one human-led pentest, the report a customer or auditor asked for. Then you keep it true as you ship. Siemba does both, from one partner.

Step 1 · we run it · scope-based

Your first pentest

A deep-dive manual test by in-house certified engineers. The signed, attestable report your first enterprise customer or SOC 2 auditor is asking for.

  • In-house OSCP, CPENT & CEH testers, never a crowd
  • Manual depth across web app, API, auth, and business logic
  • OWASP-aligned methodology, background-checked engineers under NDA
  • Signed, attestable third-party report + attestation letter
  • Satisfies SOC 2 Type II and vendor pentest requirements
Priced by scope, right-sized to your app.
Talk to a startup security expert
Step 2 · you run it · self-serve

Keep it true as you ship

Continuous autonomous testing on the same platform enterprises run, sized and priced for a startup, so your evidence never goes stale.

  • AI-native automated testing across your web app & API
  • Continuous external attack-surface monitoring on one domain
  • Every fix re-tested and flagged if it reappears, included
  • One-click SOC 2, ISO 27001, PCI DSS, HIPAA & NIST reports
  • Findings routed to Jira, Slack & GitHub, with CI/CD hooks
$100 / month · 5 tests included
See what's included

The report you can hand to a customer or an auditor

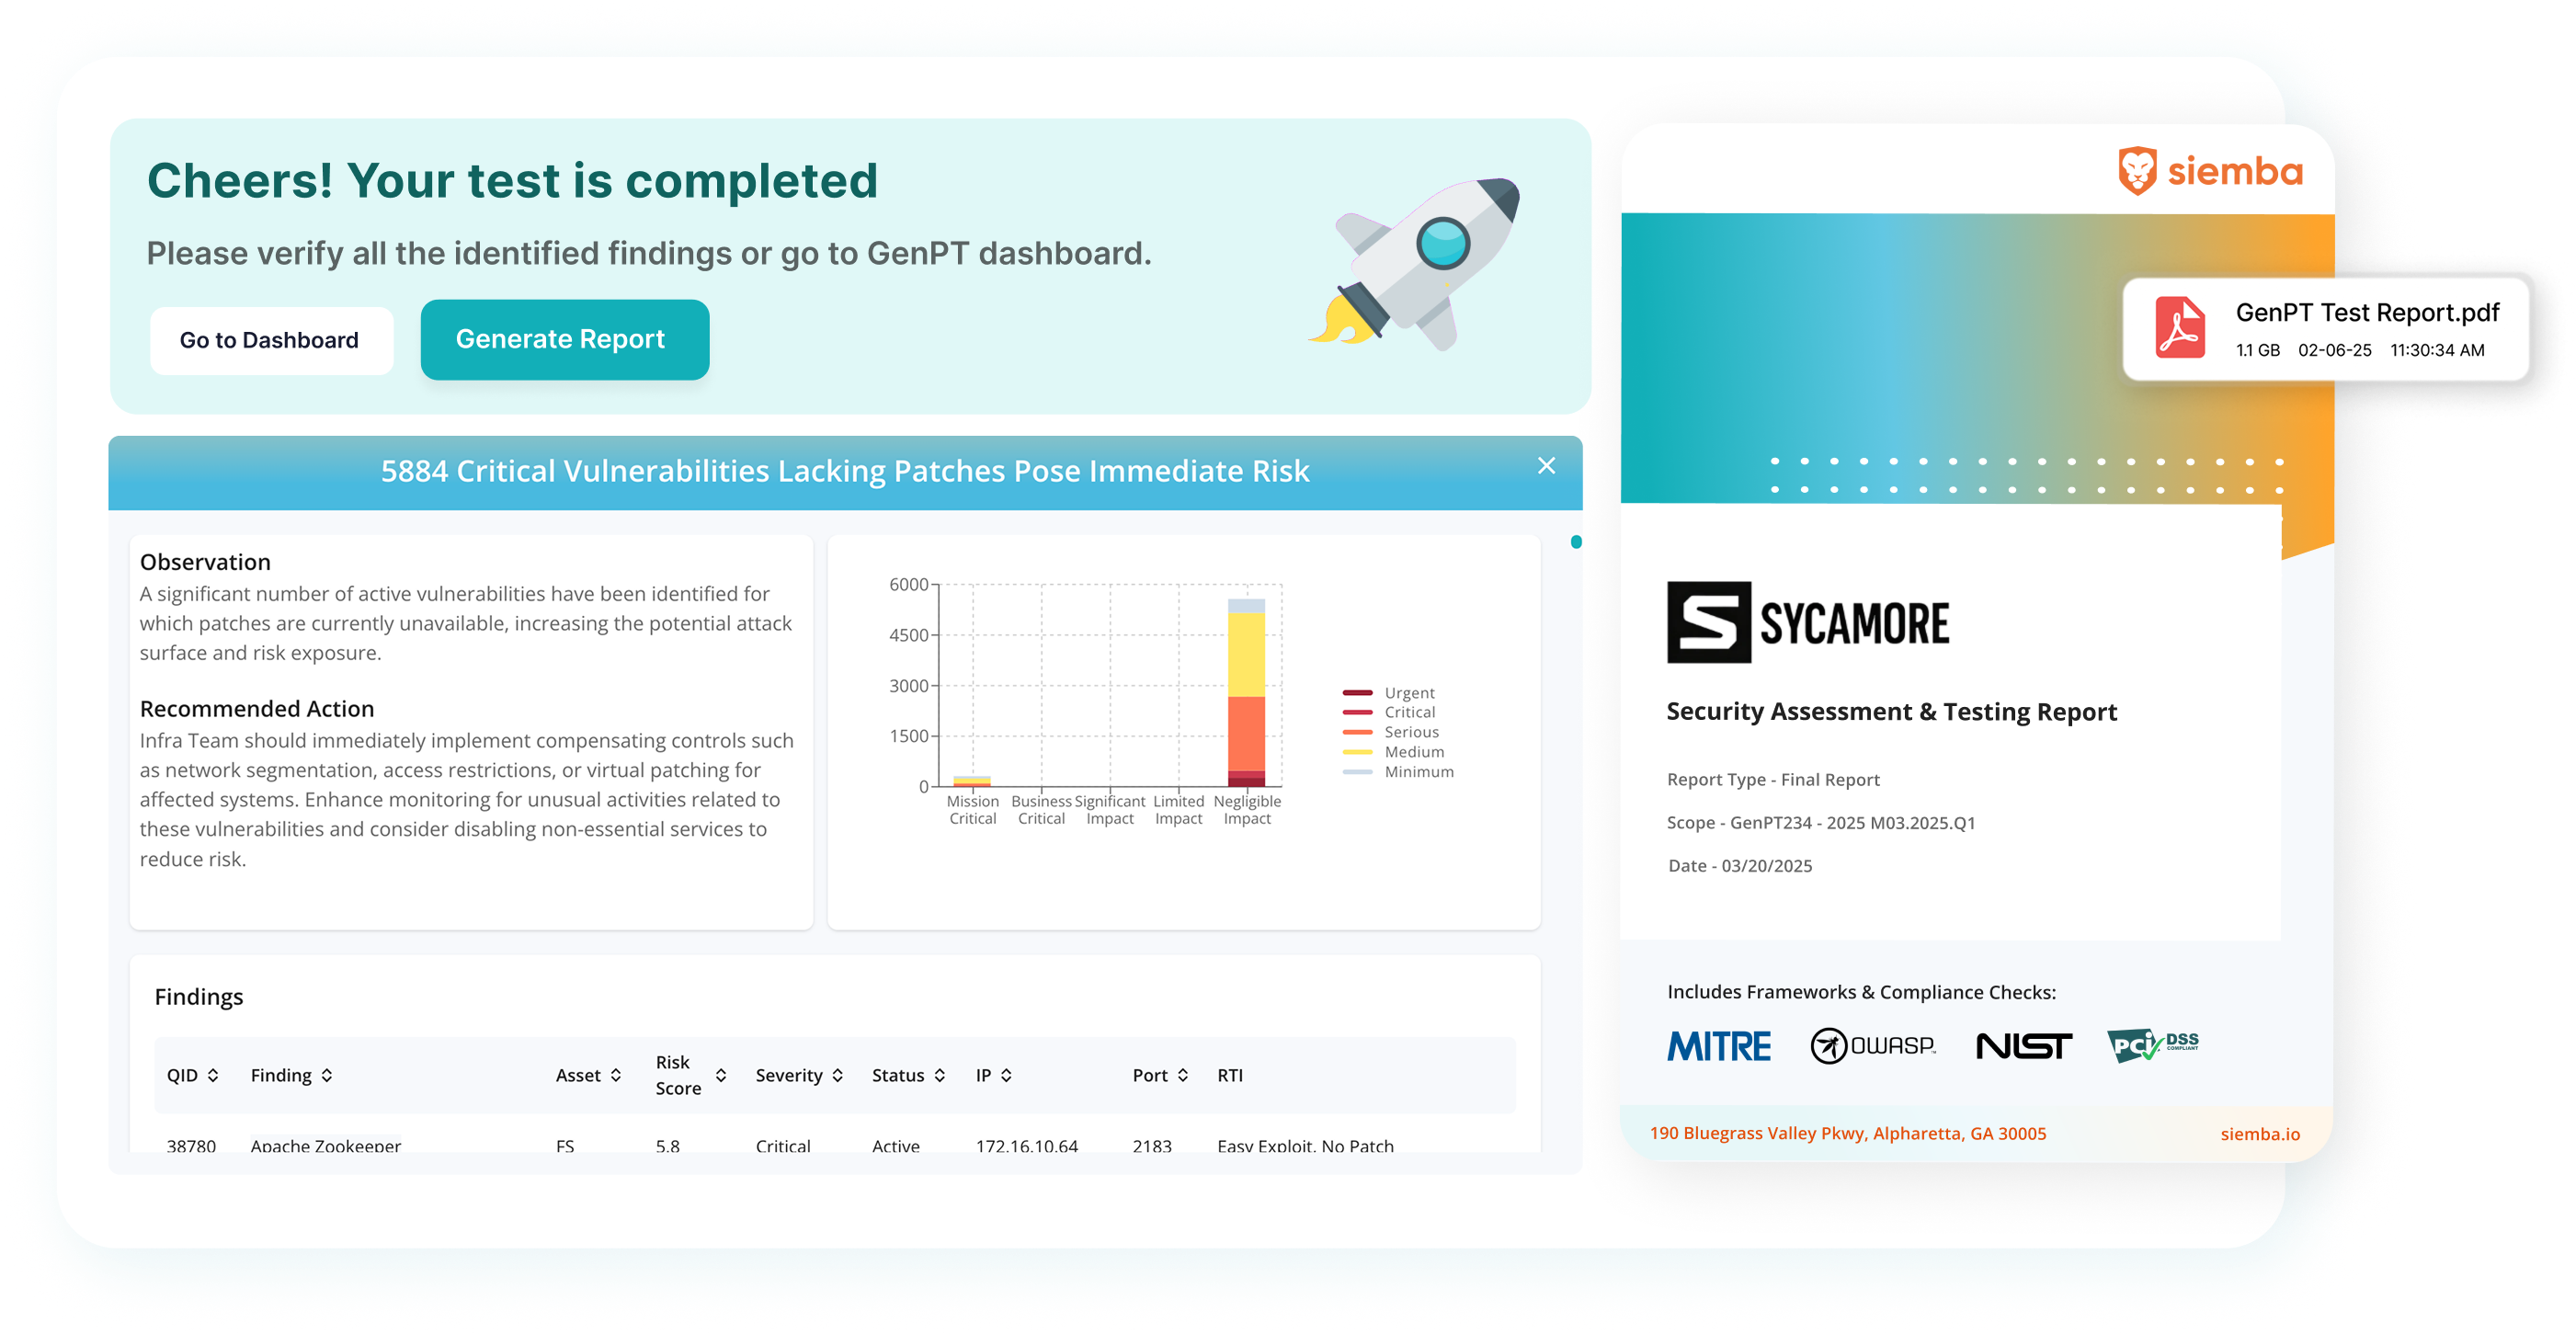
Signed penetration test report

Executive summary, findings by severity, reproduction steps, remediation guidance, and methodology, written to be read by your buyer's security team.

Attestation letter you can share

An independent letter certifying the test and the remediation of findings. The artifact enterprise procurement and auditors ask to see.

Verified Closure

Every fix is re-tested and flagged if it reappears, at no extra cost, included. A finding isn't closed until it's proven closed.

Compliance-ready evidence

One-click reports mapped to SOC 2, ISO 27001, PCI DSS, HIPAA and NIST, ready when a customer's review or your auditor needs it.

Full platform, startup price

The same platform enterprises run. Sized for a startup

$100/ month · 5 tests included

It's not a stripped-down tier. It's the full platform, right-sized to what a startup actually needs.

AI-native automated testing

Point it at a web app or API and get real, exploit-based findings back, not a scanner's guess at what might be wrong.

Attack surface monitoring

Continuous external monitoring on one domain: certificate grade, TLS protocol checks, open ports, and weak cipher suites.

Verified Closure

Every fix gets automatically re-tested and flagged if it reappears, at no extra cost, included, not an add-on.

Compliance-ready reporting

One-click evidence mapped to SOC 2, ISO 27001, PCI DSS, HIPAA and NIST, for the next customer security review.

Siemba Jira Slack

Jira, Slack & GitHub

Findings land where your team already works, plus CI/CD hooks so testing keeps pace with how often you ship.

Unlimited users

Invite your whole team (engineers, founders, whoever needs to see findings) at no extra cost per seat.

Findings you can act on, not a wall of scanner noise

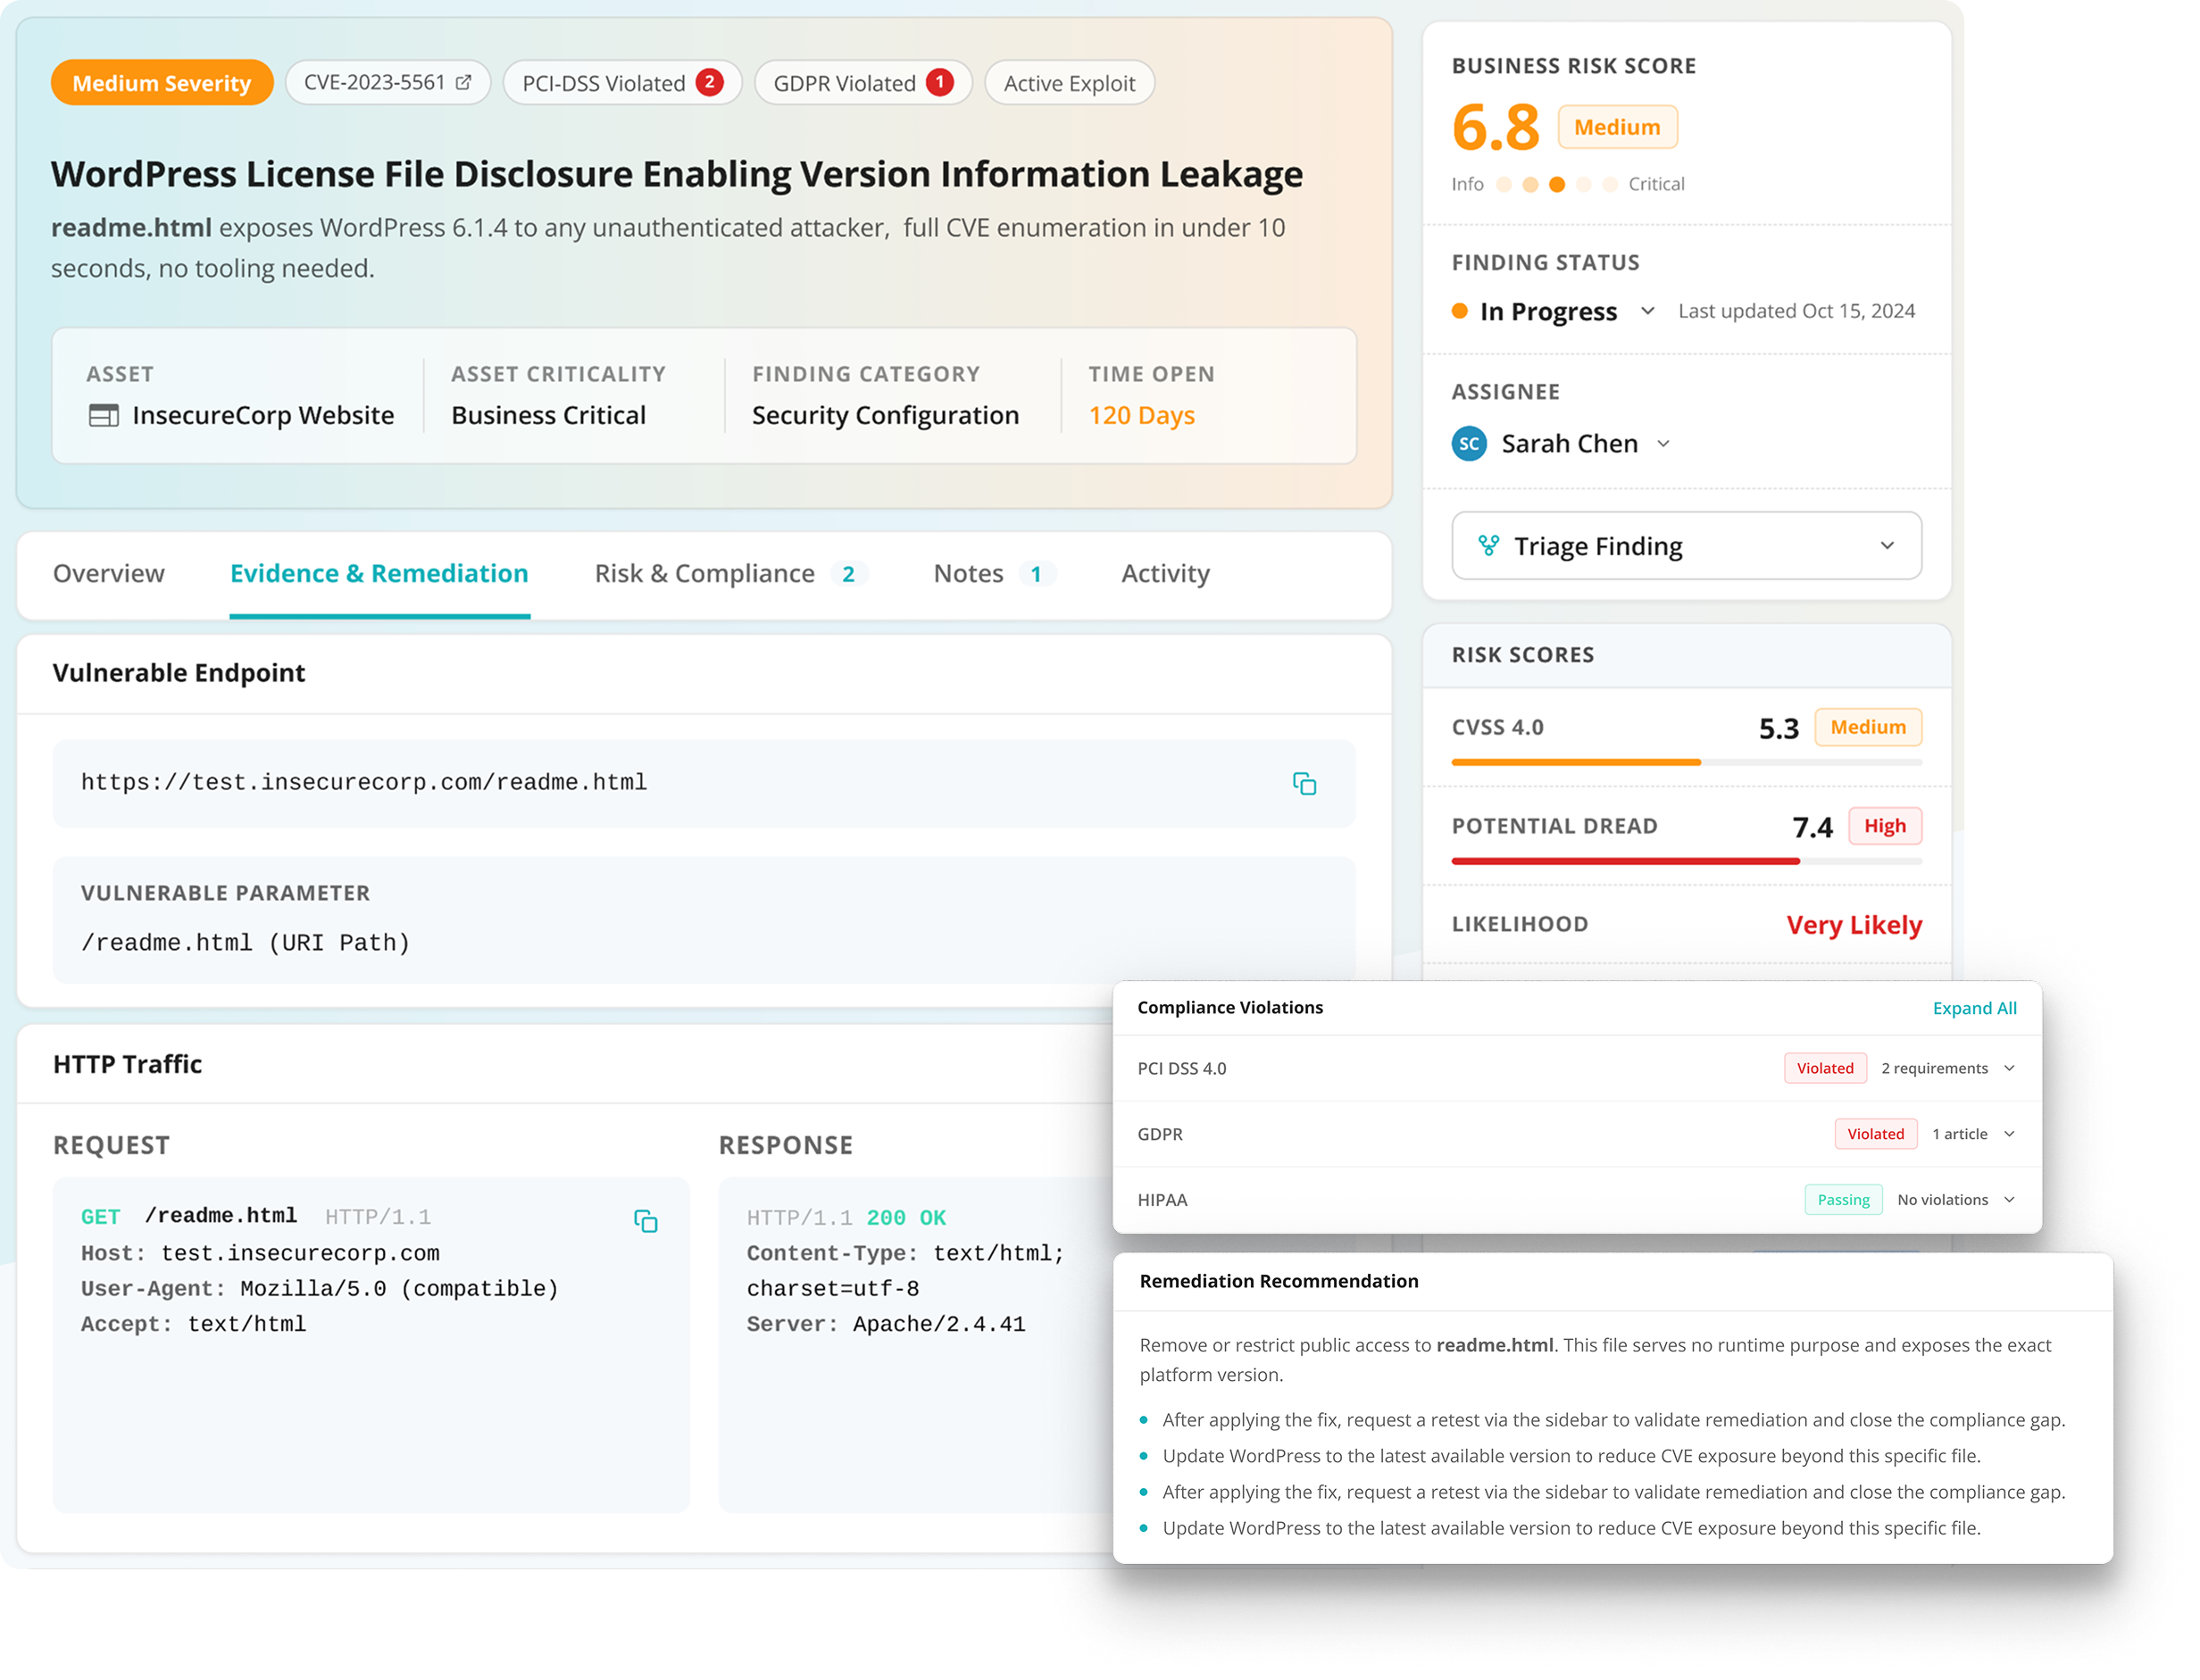
Exploit-based results with severity, remediation, and Verified Closure, in one view your whole team can see.

NEW

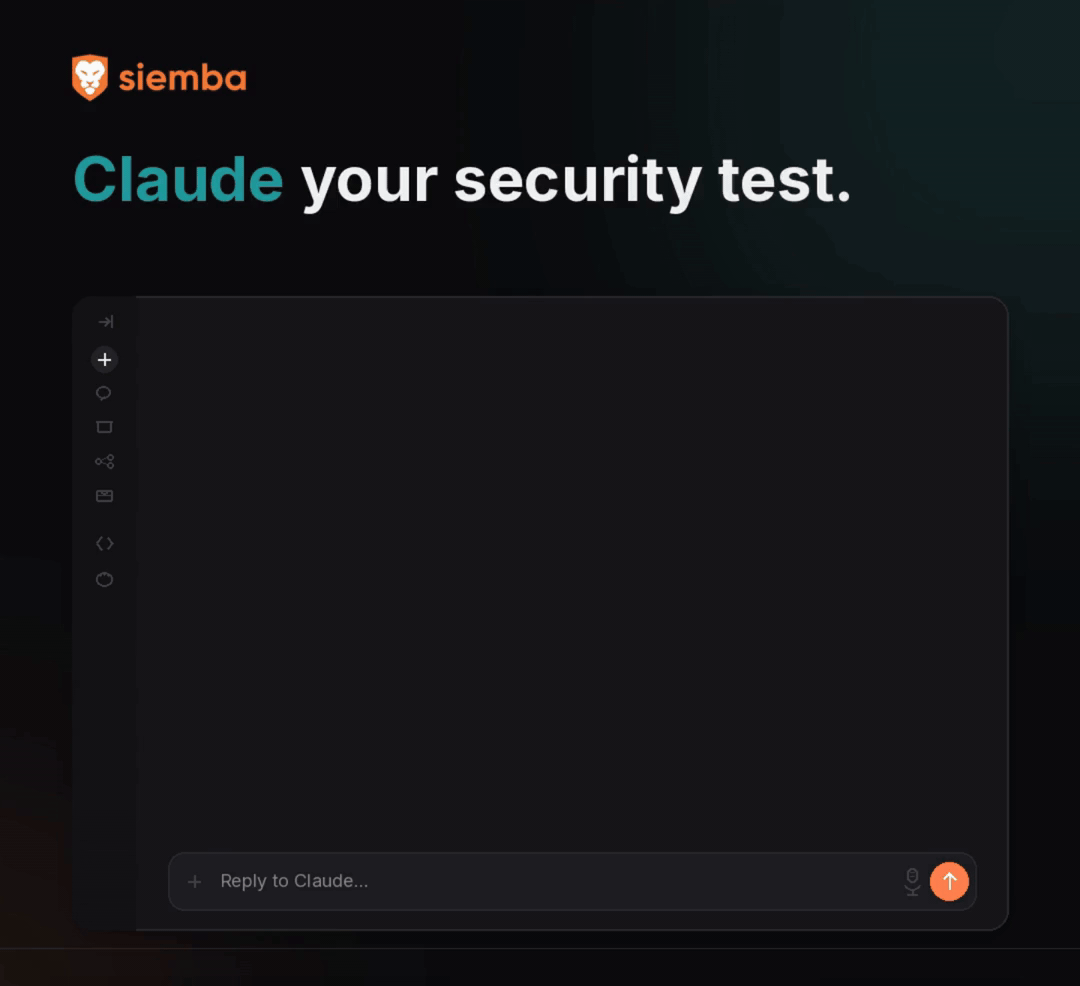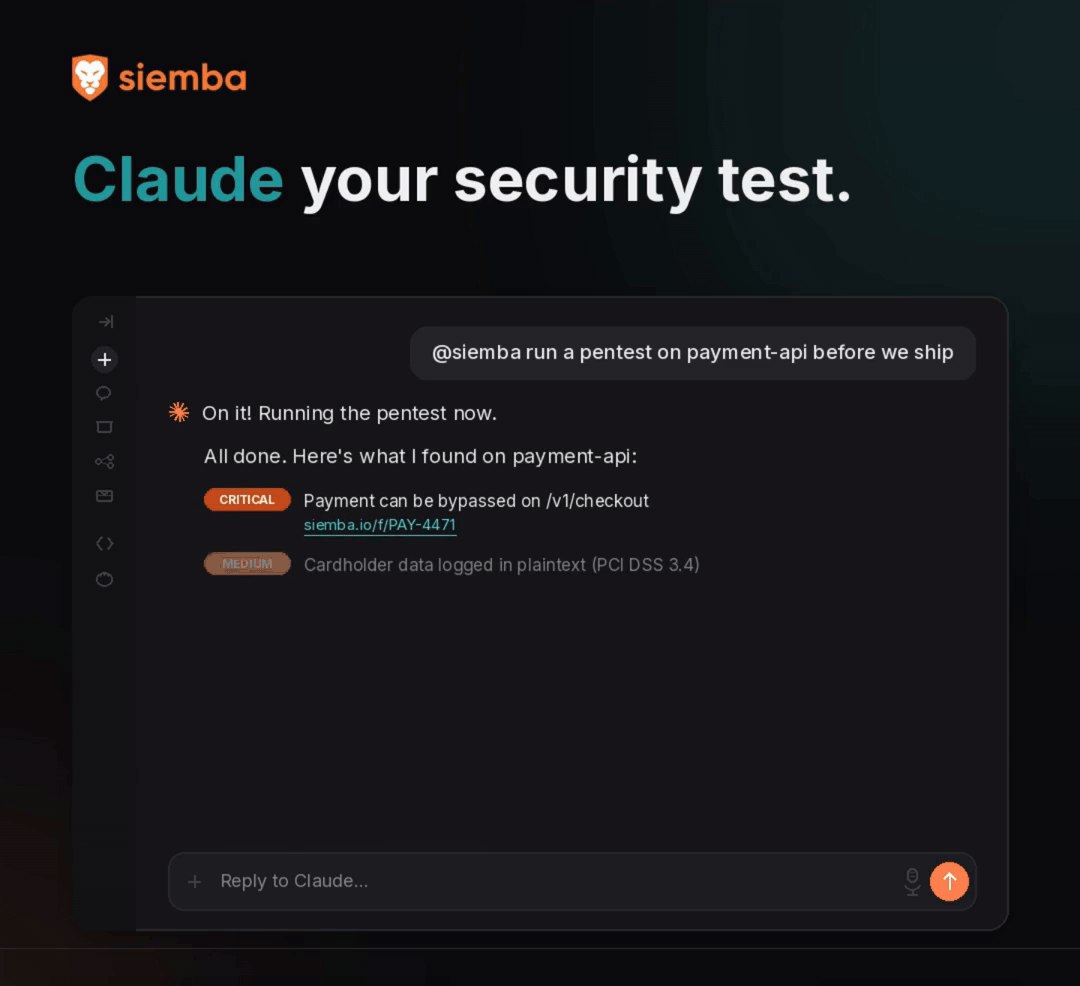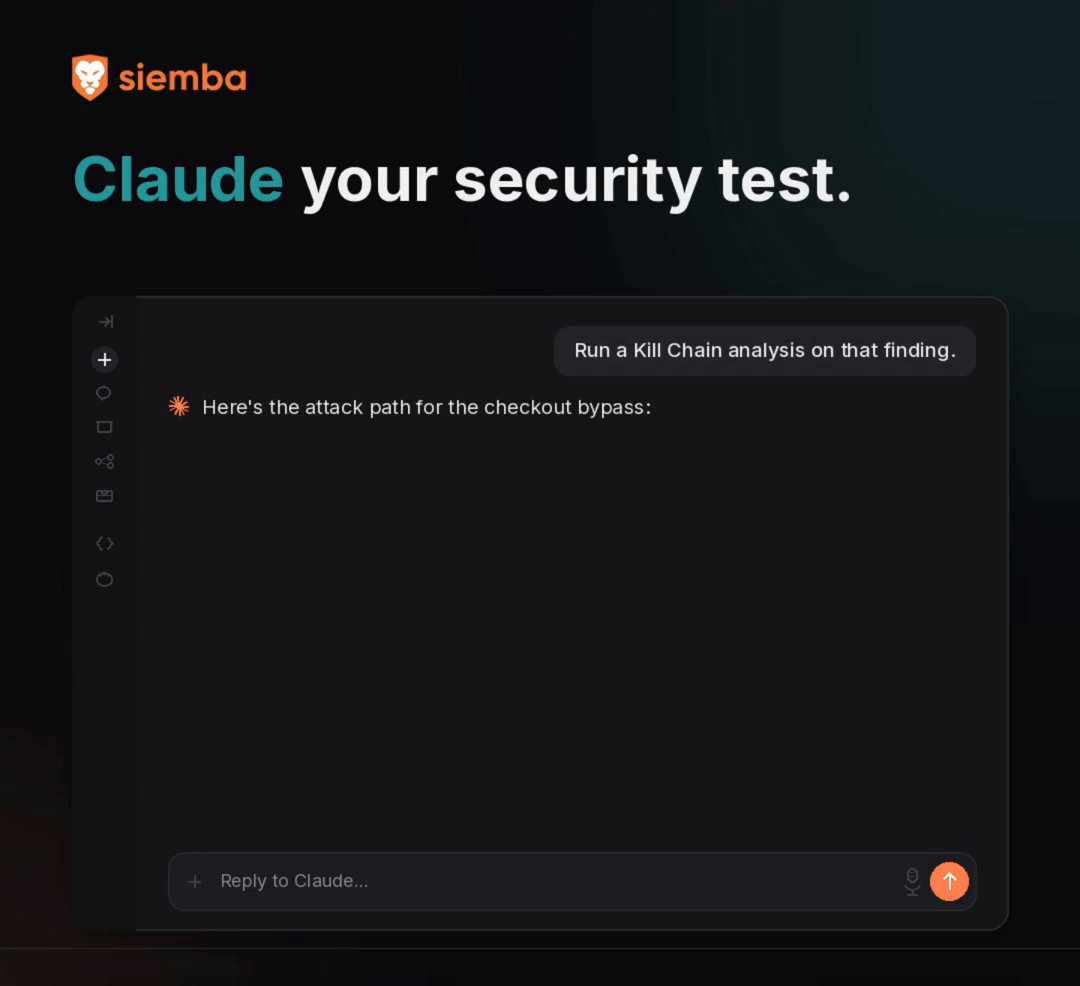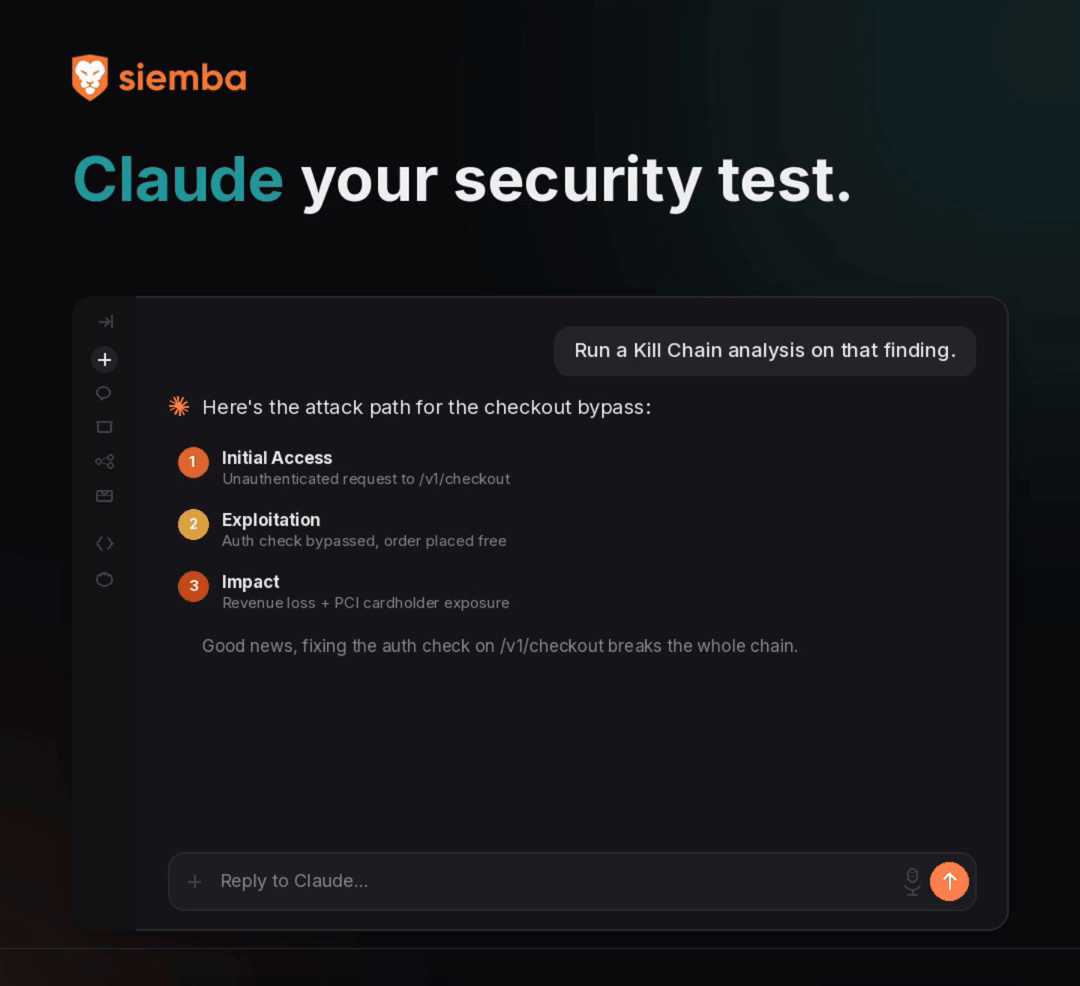
Run your pentest from your AI assistant

Prefer to work from Claude, Cursor, or any MCP client? Siemba is available as an MCP server. Trigger scans, pull findings, and scope engagements without leaving your AI client.
Claude Cursor Any MCP Client
Learn More

From stuck deal to proven closed

Talk to a startup security expert

A short call to scope your first pentest around the app, APIs and data actually in the deal. No obligation.

We run the test

Certified engineers run your first manual pentest; the platform runs continuously alongside it from day one.

Get your signed report

A signed report plus an attestation letter. Hand it straight to your customer's security team or your auditor.

Keep testing as you ship

Continuous autonomous testing keeps your evidence current, from $100/mo. Cancel anytime.

Best practices

A straight answer on when, and how, to run your first pentest

No pitch, just how we'd advise a founder or a vCISO scoping their first engagement.

When should I run one?

When the first customer or auditor asks, don't wait

The trigger is almost always external: an enterprise deal, a SOC 2 Type II audit, or a partner's third-party risk review. Start scoping the moment it appears; a good report takes days, not hours.

How do I scope it?

Scope to what you're actually selling

Test the app and APIs in the deal, the authentication flows, and the paths that touch customer data. You don't need to test everything you've ever built. You need to cover what the buyer is trusting.

One-time or continuous?

One-time clears the deal; continuous keeps it true

A one-time pentest unblocks the contract in front of you. If you ship weekly, continuous testing keeps that evidence current so the next review doesn't start from zero.

What does an auditor need?

An independent report, not a scan printout

Auditors and enterprise buyers want a signed third-party report and an attestation of remediation. A raw scanner export doesn't satisfy a SOC 2 or PCI DSS pentest requirement.

What teams say about working with us
★★★★★
Taught us how to think about security.
Siemba didn't just find issues, they taught us how to think about security.
Alvin Allen
Head of Cybersecurity · FRONTSTEPS
Customer
★★★★★
Powerful all-in-one solution.
Uncovered assets we missed. Risks validated in hours, not weeks.
Arun C.
Verified · G2
G2
★★★★★
Great end-to-end tool for small teams.
Structured reports within minutes. Zero heavy overhead.
Mevin B.
Verified · G2
G2
★★★★★
Great end-to-end security platform.
Immediate visibility. Speed and ease of use, all in one.
Anandu N.
Verified · G2
G2
★★★★★
"Pentesting on steroids."
Continuous, automated, and actually actionable.
Security Professional
LinkedIn Review
LinkedIn

The things startups ask us first

Okay, what does this actually cost?

The continuous platform is $100/month with 5 tests included, a startup rate you won't find on our public pricing page. Your first manual pentest is priced by scope, right-sized to the app and APIs in your deal. Talk to a startup security expert for a scoped quote.

My first customer is asking for a pentest report. What does that mean?

They want independent proof your application has been tested for security flaws by a qualified third party. In practice that's a penetration test: certified testers attempt to exploit your app the way an attacker would, then deliver a signed report of what they found, how severe it is, and what you fixed. It's a normal part of enterprise vendor reviews, and we'll walk you through exactly what your customer is likely to want to see.

Is an automated/AI test enough for my SOC 2 auditor, or do I need a manual one?

For an independent third-party pentest requirement (SOC 2 Type II, PCI DSS, or a customer's security review), you generally need a human-led manual pentest with a signed, attestable report. That's what our Expert Engagements deliver. The continuous platform keeps you covered between engagements and produces one-click compliance evidence, but the attestable report is the manual piece.

Do I get an attestation letter I can share with customers?

Yes. Alongside the full report you get an attestation letter certifying the test and the remediation of findings. The artifact you can hand to a customer's procurement or security team, or to your auditor, without exposing sensitive detail.

What do I put in a vendor security questionnaire?

The questions that trip startups up are usually about how often you run third-party testing, whether you have a recent pentest report, and how you remediate findings. A Siemba engagement answers all three: a dated third-party report, an attestation of closure, and continuous testing you can point to as an ongoing cadence. If you're staring at your first questionnaire, we'll help you map your answers.

What happens to unused tests at the end of the month?

Your 5 monthly tests refresh each billing cycle. [Placeholder: confirm rollover policy: do unused tests roll over or reset?]

What if I need more than 5 tests in a month?

Additional test bundles can be purchased whenever you need more headroom. [Placeholder: confirm bundle size and price.] If you're consistently running more, that's usually the signal to talk about a larger plan.

How long is this discounted rate available?

[Placeholder: confirm terms: is the startup rate locked for the life of the account, time-limited, or tied to a stage/size threshold?] Whatever you start on, we'll be clear about it up front, no surprise price jumps.

Can I cancel anytime?

Yes. The platform subscription is month-to-month, cancel anytime, no lengthy contract. A one-time pentest is a one-time engagement with no ongoing commitment.

Is there anyone I can actually talk to?

Always. Startups get a real startup security expert to scope your first pentest and help you read a customer's questionnaire, not a chatbot and not a generic sales rep. Book a time to talk.

Your attack surface is being mapped right now. Make sure it's you first

Book a live walkthrough or run a free scan today. No lengthy contracts, no hidden fees, unlimited automated revalidation included from day one.